Third-party risk management for NIS2.
Suploris is supplier risk management software from Austria. Check the information security of your suppliers, understand every grade and prove your due diligence under NISG 2026.
- Data stays in the EU
- Free for suppliers
- Every grade explained
For your whole supplier list: Start for free
Why B?
Evidence for tier 1
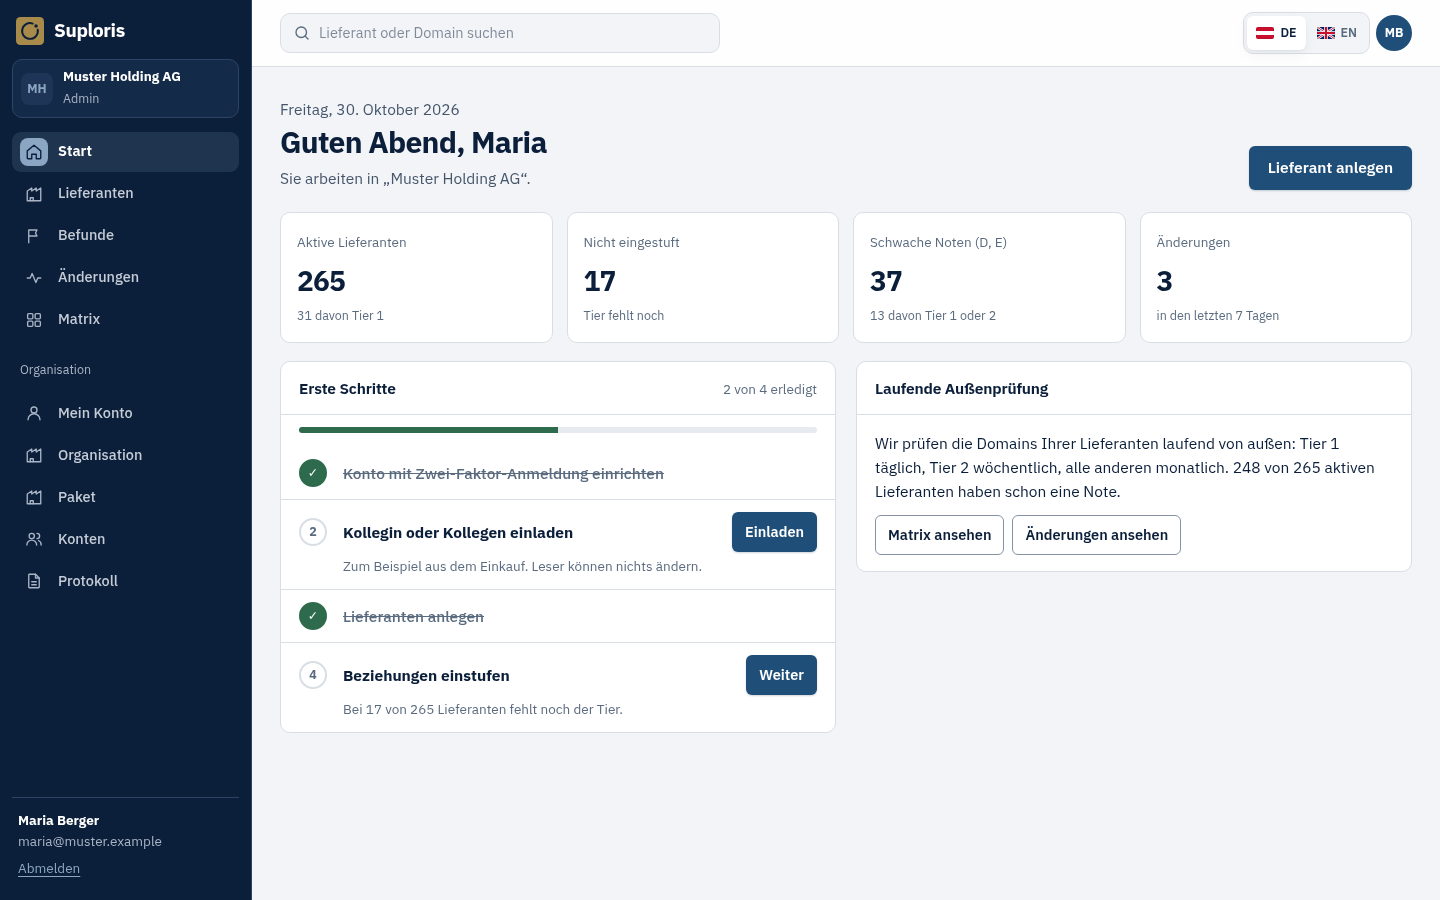
One profile per supplier. For every risk.
All risk areas in one profile, so you do not have to maintain several tools. Information security is part of every plan; you add further areas as modules.
- Information security
Supplier risk assessment with outside-in check (email protection, encryption), security questionnaire for NISG 2026, evidence.
in every plan - Compliance and sanctions
Sanctions screening against the EU sanctions list and lists of the UN, the US and the UK.
Module - Finance
Supplier insolvency and credit standing from official sources such as the Austrian insolvency register.
Module - Data protection
Data processing agreement (DPA), subprocessors, transfers to third countries.
Module - Resilience
Risk of outage, alternative suppliers, concentration risk from a few providers.
Module - ESG and human rights
Country risks, certificates, supply chain due diligence (CSDDD).
Module
From Austria, for Europe.
- Built in Austria
By Neuralis GmbH i.G., with experience in information security.
- Data stays in the EU
Your data is stored in data centres in the EU. We name our service providers openly.
- GDPR from the start
Data processing agreement, retention periods and a log of every change.
- Support in English and German
Interface, templates and help in your language.
- Passive checks only
We only see what is public. No port scans, no attacks.
Since 1 October 2026, the supply chain is part of security.
- Austria's NISG 2026 requires measures for the security of the supply chain.Section 32(4)(d) NISG 2026, Federal Law Gazette I No. 94/2025. Checked on 29 Oct 2026.
- Attackers often come in through service providers, software and remote maintenance of suppliers.
- A spreadsheet does not show which supplier is a risk today.
Four steps from supplier list to proof.
Discover
Upload your supplier list. Suploris matches domains and finds duplicates.
Classify
Five questions on importance give a suggested tier from 1 to 4.
Assess
Outside-in check, questionnaire and evidence give a grade with reasons.
Prove
A report shows auditors and the authority whom you checked, when and how.
A grade that explains itself.
Every grade shows what it is made of, which source supports it and how old the data is. You set weights and rules yourself.
Like an inspection sticker, the grade is valid for a set time only. Old data counts less until the next check.
Example
Why B?
Schema “Information security tier 1”, version 3- Email sender protection in monitoring mode only minus 8, DNS 29 Oct
- Certificate valid, TLS 1.3 passed, 29 Oct
- Multi-factor sign-in for remote maintenance in place, answer 14 Oct
- Emergency plan not tested minus 12, answer 14 Oct
- ISO 27001 certificate, valid until 03/2028 checked 15 Oct
Knock-out rule not triggeredWithout a contact person for security incidents, the best possible grade would be C.
Free for suppliers.
Suppliers fill in their profile once and share it with as many customers as they like. That saves work on both sides.
- See findings of the outside-in check, correct them and upload evidence.
- Questionnaires in English or German, pre-filled with answers from earlier questionnaires.
- Decide which customer sees which documents.
Fixed prices up to 500 suppliers, without an implementation project.
Free
To try it out.
€0
- Up to 10 suppliers
- Outside-in check with grade and calculation
- One questionnaire “NISG short”
- 2 users
Team
For security and procurement in mid-sized companies.
€3,900 a year
- Up to 100 suppliers
- Complete security: questionnaires, findings, NISG report
- Unlimited users
Business
For larger supplier bases and several risk areas.
€9,900 a year
- Up to 500 suppliers
- Austrian company data filled in automatically
- Sign-in with your company account (SSO)
- API and webhooks as an add-on
Enterprise
For corporations and groups.
On request
- More than 500 suppliers
- API, webhooks and lifecycle included
- Contract on your terms
Annual prices in euros, excluding VAT. You pay by the number of your active suppliers; users are unlimited from Team upwards. Modules such as compliance or supply chain are added per plan. Above 500 suppliers we prepare a quote. Suppliers never pay.
Frequently asked questions
What is third-party risk management (TPRM)?
Third-party risk management means finding, assessing, monitoring and documenting risks from suppliers. It covers information security, sanctions, insolvency, data protection and ESG. It is also called supplier risk management or vendor risk management.
What does Austria's NISG 2026 require for suppliers?
Essential and important entities must take measures for the security of their supply chain (section 32(4)(d) NISG 2026). This includes the cybersecurity practices of their providers. Suploris helps with grade and calculation, questionnaire and evidence. Source checked on 30 October 2026.
Is the self-test legal?
Yes. The self-test only reads data that every browser and every mail server sees anyway. It does not look for open ports, does not try any logins and does not fill in forms.
What exactly do you check?
Protection against forged senders (SPF, DMARC, MTA-STS) and the encryption of the website. Also security headers, the security.txt contact, DNSSEC and the expiry date of the domain.
Where is my data stored?
In data centres in the EU. We use Cloudflare for access and bot protection. The privacy policy lists all details.
Does my supplier see that I checked them?
No. The supplier only sees a request with our identifier. Results cannot be found publicly and expire after 7 days.
I am a supplier. How do I object to the check?
Write to us via the self-test info page. We will put your domain on the exclusion list.
Does Suploris replace an ISO 27001 certification?
No. Suploris helps you assess suppliers and collect evidence. Certification remains the job of an accredited body.
Who is Suploris for?
For companies in Austria, Germany, Switzerland and the rest of Europe. They use it to assess suppliers under NISG 2026 and NIS2.
Does NIS2 apply to my suppliers?
The duty lies first with essential and important entities. But they must manage the security of their supply chain (Article 21(2)(d) of the NIS2 Directive). So they ask their suppliers for evidence. In the free supplier portal, suppliers answer these questions online.
How much does supplier risk management software cost?
With Suploris you pay by the number of your active suppliers. Free costs €0 for up to 10 suppliers. Team costs €3,900 a year for up to 100 suppliers. Business costs €9,900 a year for up to 500 suppliers. Above 500 suppliers we prepare a quote. Suppliers never pay.
Does Suploris screen sanctions lists?
The compliance and sanctions module is in preparation. It will screen the supplier and its parent company. Sources are the EU financial sanctions list and lists of the UN, US and UK. A match only counts once a person confirms it.
Does Suploris help with DORA?
In part. The outside-in check and the questionnaire cover the information security of ICT providers. Suploris does not currently offer its own DORA questionnaire or the DORA register of information.
How quickly can we start?
On the same day. You upload your supplier list as an Excel or CSV file, map the domains and the outside-in check begins. No implementation project is needed.
Enterprise for more than 500 suppliers.
We prepare a quote on your terms and show you Suploris on your real suppliers. Free and without obligation, in English or German.
Questions in advance? Write to kontakt@neuralis.at.